Strong cyber security fail fast if an intruder walks into your server room. In Tier III and Tier IV sites, one breach can cause major downtime. It leads to steep legal fines and destroys client trust. Managing large sites requires constant effort against internal and external threats.
Why old security methods fail:
- Perimeter systems often miss insider threats, stolen badges, and unescorted guests.
- Separate camera systems create blind spots and delay real-time threat detection.
- Paper visitor books make compliance audits hard and slow down emergency responses.
Modern data center security needs one clear plan. It must connect access rules, biometric checks, and smart video systems. Linking Tier 3 data center access control with main monitoring gives full visibility. This approach tracks worker shifts, meets labor laws, and protects data privacy.
- Combined security cuts human error and speeds up emergency responses across all zones.
- Automated logs simplify compliance audits for corporate, financial, and government rules.
- Integrated systems protect your hardware investments without adding extra work.
- Central management reduces admin tasks and gives security teams live threat data.
Next, we review the step-by-step physical security plan needed to protect key infrastructure.
What Are the Core Physical Security Requirements for Tier III and Tier IV Data Centers?
Core security rules for top facilities blend physical barriers, zone checks, camera feeds, and automated logs. Strong data center physical security protects critical work while keeping uptime high. Tier III sites allow routine maintenance without downtime. Tier IV sites demand full fault tolerance with no single failure point. To meet Indian laws, modern designs must stay secure at every layer.
- Perimeter and Access Security: Multi-layer checks using biometrics, smart cards, and heavy vehicle gates.
- Continuous Surveillance: Full camera coverage linked with live video analytics, attendance logs, and door records.
- Compliance Alignment: Secure audit trails that meet RBI, IRDAI, MeitY, and DPDP Act rules.
Why Does Concurrently Maintainable Infrastructure Require Active Access Control?
Tier III sites allow planned maintenance without turning off server gear. Yet, human error during routine service still causes sudden downtime. Strong Tier 3 data center access control separates active work areas from live hardware.
- Zonal Isolation: Limit technician access only to the exact server bays being serviced.
- Path Segregation: Block accidental access to backup systems during routine repairs.
- Power Resilience: Dual-power controllers keep door readers working during main power switches.
Without active access rules, a technician could easily unplug a live power line by mistake.
How Do Tier IV Fault Tolerant Standards Impact Physical Security Protocols?
Tier IV designs remove single points of failure across power, cooling, and security systems. Every door, reader, and camera must use this redundant setup.
- Redundant Controllers: Dual-node door panels stay online even if the primary network drops.
- Compartmentalization: Physical walls isolate backup generators, fuel tanks, and power transformers.
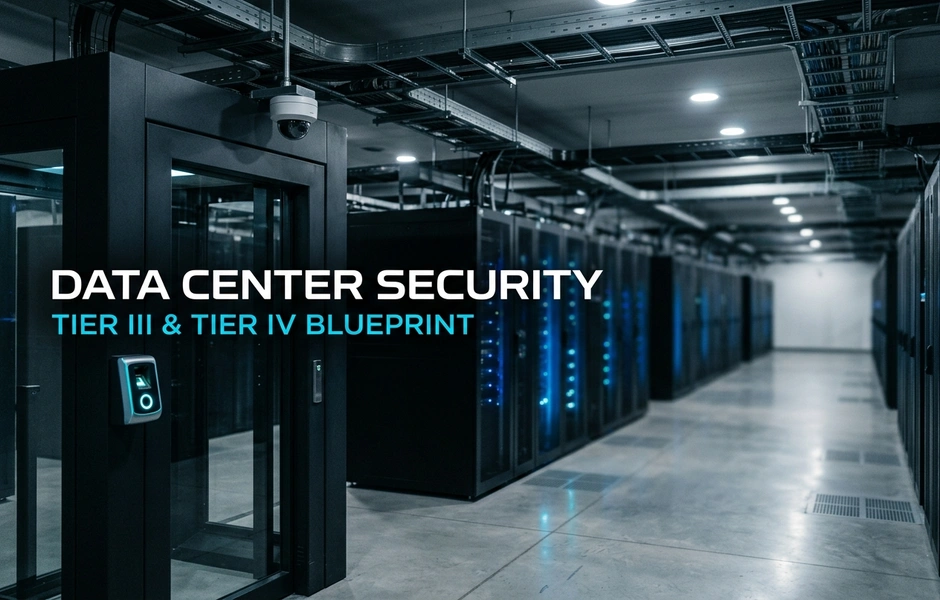
- Vault-Level Control: Server rooms need a mantrap and 2FA for data centers to block tailgating.
Unified security protects physical gear while automating regulatory reports. Matrix offers access control, video monitoring, and attendance in one reliable setup.
Next, we explore how to deploy high-availability controllers across multi-tenant sites.
How Do You Implement a 5-Zone Perimeter-to-Rack security Layer?
Building a five-zone security requires layering security from the outer fence down to server racks. Each zone acts as a checkpoint to check IDs and monitor movement. This layout keeps protection strong across all tiers.
- Zone 1 (Perimeter Fencing): Controls car entry using heavy gates and long-range cameras.
- Zone 2 (Building Facility Entry): Checks all incoming staff and handles visitor sign-ins.
- Zone 3 (White Space Boundary): Isolates key server rooms with interlocking doors.
- Zone 4 (Server Room Interior): Tracks movement in server aisles using live video analytics.
- Zone 5 (Cabinet Level): Locks individual rack handles with biometric or card scanners.
Linking cameras with Tier 3 data center access control matches card scans with live video. This multi-layer design removes single points of failure in data center physical security.
Zone 1 & 2: How Should You Secure Outer Perimeters and Building Entrances?
Outer borders face harsh weather and unvetted traffic. Sites in places like Navi Mumbai need tough security that can withstand heat, dust, and coastal humidity.
Modern setups use ANPR gates, boom barriers, and tough IP cameras with high protection ratings. These devices keep recording during power switches and generator starts.
At building doors, security teams must check IDs strictly to manage crowds and changing shifts.
- Old System vs. Modern System: Old setups use paper logs and basic badges. Modern systems use biometrics, escorted visitor rules, and no-phone policies.
- Visitor Governance: Short-term workers get timed badges valid only for specific areas.
This setup helps key facilities satisfy local DPDP Act rules and compliance standards easily.
Zone 3 & 4: Why Are Mantrap and 2FA for Data Centers Crucial at White Space Boundaries?
White space boundaries protect main servers from physical damage and unauthorized entry. Simple door locks leave sites open to tailgating and accidental breaches.
Using a mantrap and 2FA for data centers stops this risk through interlocking doors. The outer door must close before the inner door unlocks.
- First Authentication: The user scans a smart card at the outer door.
- Interlocking Containment: The user steps inside while weight sensors verify only one person is present.
- Second Authentication: The user scans a fingerprint or face to open the inner door.
Unified zone security protects key workloads and simplifies compliance audits. Matrix provides integrated access control, video, and attendance on one controller platform.
Next, we will inspect cabinet locks and audit logging.
How Should You Secure Server Rooms and Individual Equipment Racks?
Securing server rooms and equipment racks requires a multi-layer security plan. Facilities must combine room borders with detailed rack-level controls. Insider threats, vendor errors, and human mistakes cause major downtime in dense server rooms. To stop accidental outages and bad actors, facilities use multi-factor checks, aisle video, and smart cabinet locks. Strong data center physical security relies on strict ID checks before anyone touches server hardware. Using advanced Tier 3 data center access control ensures only approved engineers enter assigned server rows. Linking smart handles with central logs creates a complete audit trail. This framework limits internal security risks and protects sensitive gear from physical attacks.
What Are the Key Standards for Server Room Surveillance Design?
Good server room surveillance design removes blind spots along narrow server rows. Dense white spaces need smart camera placement to handle low light and glare.
Key camera rules include:
- Aisle Coverage: Place wide-angle cameras at both ends of every server row.
- Lighting Management: Use wide dynamic range sensors to adjust to lighting shifts.
- Hardware Compliance: Choose cameras that meet BIS and STQC cyber rules to prevent device hacks.
- DCIM and Security Integration: Connect live video feeds to DCIM platforms for better threat tracking.
Industrial IP cameras handle humidity and dust in regional hubs like Navi Mumbai and Chennai. Native sensors stop hardware tampering while saving clear video across every hall.
How Do Cabinet Controls and Two-Person Integrity Protect Colocation Spaces?
Colocation sites host gear for many clients in shared rooms. Room locks alone cannot stop someone from opening a neighbor’s rack.
Smart cabinet locks put card readers and biometric scanners right on rack handles. Enforcing two-person rules adds strong control for high-security rooms.
- Dual Authorization: Two approved techs must scan badges together to open key cabinets.
- Time-Bound Rules: Badges only open cabinet doors during scheduled repair windows.
| Feature | Old System | Modern System |
| Rack Access | Metal keys with paper sign-in sheets | Biometric handles with live audit logs |
| Integrity Enforcement | Single tech enters with no monitoring | Automated two-person entry checks |
Detailed rack security stops human errors from taking down enterprise servers. Matrix provides an all-in-one system with access control, video, and attendance. Operators get automatic reports and lower total costs.
Next, we will explore how unified security software joins access logs and video onto one dashboard.
Why Is Native DCIM and Security Integration Essential for Physical Security?
Split security systems create risky blind spots in modern data centers. Facilities need live visibility across physical and utility setups. Native DCIM and security integration connects door events with power, cooling, and rack metrics. Linking access control with facility dashboards stops physical entry from causing unseen cooling or power outages.
Consider these key benefits:
- Real-time Event Correlation: Link unauthorized door opens to local rack heat alarms instantly.
- Single-Pane Management: View video feeds, door states, and cooling status on one screen.
- Automated Incident Response: Lock server room doors automatically when heat spikes or break-ins happen.
Using unified data center physical security keeps Tier 3 data center access control aligned with uptime goals.
How Does Seamless Software Integration Bridge DCIM and Security Workflows?
Old setups rely on split systems from different vendors that require expensive custom code. They cannot share threat data easily. Modern systems use open APIs and SDKs to link platforms smoothly. DCIM integration allows door controllers, cameras, and DCIM systems to share live data.
- Access Event Logged: A technician scans two-factor credentials at a server room door.
- Environmental Trigger: The DCIM platform detects a sudden temperature rise in that aisle.
- Correlated Video Verification: Security staff review live video linked to that exact door scan.
Unified stacks from one vendor streamline daily operations. They lower ownership costs while breaking down system silos.
How Do Unified Audit Trails Simplify Regulatory Audits and Compliance Reporting?
Manual logbooks are slow, error-prone, and fail during compliance reviews. Data centers face strict audits under corporate rules, local laws, and DPDP Act guidelines. Unified platforms automatically combine attendance, access attempts, and video clips into one log.
- Tamper-Proof Logging: Records every card scan, door request, and biometric check.
- Integrated Video Bookmarks: Links saved video directly to exact timestamped entry logs.
- SLA Compliance: Proves physical security compliance during client audits and official reviews.
Unified security eliminates audit stress by building clear reports instantly. Matrix provides a complete platform combining access control, surveillance, and time-attendance \[domain\_metadata\]. Managers gain full operational control and easy audit readiness.
Next, we will cover how to plan perimeter security for edge and hyperscale sites.
How Do You Manage Workforce Access and Contractor Governance 24/7?
Managing worker access around the clock requires combining access control, attendance, and video into one system. Rotating shifts and outside contractors add risks if tracked on paper. Strong data center physical security relies on auto-updated shift rules, biometrics, and clear contractor onboarding.
To maintain total control:
- Link access badges directly to active work schedules.
- Require biometric scans to prevent badge sharing.
- Automate contractor check-ins with timed visitor badges.
How Can Integrated Time-Attendance Prevent Identity Misuse and Proxy Punching?
Linking attendance hardware with Tier 3 data center access control enforces role-based access by shift time. Off-shift workers and unapproved vendors cannot enter server rooms, even with valid cards.
- Biometric eKYC Integration: Checks contractor IDs against official databases during onboarding to follow labor laws.
- Anti-Proxy Logic: Multi-factor biometrics stops workers from clocking in for missing colleagues.
- Zonal Restriction: Keeps technical staff inside their assigned work zones during set hours.
What Hardware Specs Ensure Reliability During Grid Instability?
Generator switches can reboot sensitive security hardware. Data centers need rugged components that stay online during severe power fluctuations.
Key features include:
- Durability Standards: Door panels with high MTBF ratings over 100,000 hours ensure continuous uptime.
- Power Resilience: Redundant PoE switches stop system reboots during power transfers.
- Fail-Secure Locking: Ensures server room doors stay locked if power drops completely.
- Environmental Protection: Industrial IP ratings protect outdoor readers from dust and rain.
Integrated hardware removes security gaps while simplifying compliance. Matrix provides single-platform management for dependable data center security.
Next, we will review how to optimize server room surveillance design for total visibility.
Conclusion: Building a Resilient Data Center Security Foundation
Building a strong security foundation requires combining video surveillance, access control, and attendance into one system. Deploying robust Tier 3 and 4 data center access control alongside multi-layer zone security transforms security from a basic cost into a real business advantage.
Securing Tier III and Tier IV data centers takes much more than outer gates and isolated cameras. High-availability sites need a strong, unified data center physical security plan. Using a 5-zone security protects critical assets from outer fences down to individual server racks.
A strong security design rests on four main pillars:
- Multi-layer zone security that protect sensitive white spaces.
- Strict ID checks using multi-factor login workflows.
- Direct links between physical security and DCIM platforms.
- Rugged hardware that stays online during sudden power switches.
Unifying your security setup cuts operational risk, speeds up compliance audits, and protects client SLAs. Audit your security layout today to remove hidden coverage gaps and ensure continuous facility uptime.
Connecting video feeds with Tier 3 data center access control and attendance stops blind spots across every hall. Enforcing a mantrap and 2FA for data centers blocks tailgating at room borders. Careful server room surveillance design and smart cabinet locks protect shared racks from internal threats and user mistakes.
Frequently Asked Questions
What is the difference between Tier III and Tier IV physical security requirements?
Tier III data centers require concurrently maintainable access control. This design lets staff service equipment without dropping security coverage. Tier IV demands full fault tolerance using dual network cables and backup power. Every door panel, camera, and access point must survive a single failure without losing protection.
How does a mantrap prevent tailgating in server rooms?
A mantrap uses interlocking doors between two physical points. The system keeps the inner door locked until the outer door closes fully. A person must then pass a two-factor or biometric check inside the chamber. This process ensures only one verified person enters key server areas at a time.
Why should video surveillance integrate directly with DCIM and access control?
Direct integration links card scans instantly with camera feeds. When a cabinet opens or an alarm triggers, guards see live video on their main dashboard. This combined view speeds up incident response. It also creates clear audit records for regulatory compliance across critical infrastructure.
How can data center physical security systems maintain uptime during power switchovers?
Data centers use industrial door controllers with dual power feeds and battery backups. These parts keep access panels running smoothly during power outages and generator starts. Smart locks use fail-secure designs. This hardware layout keeps perimeter gates and rack locks secure during sudden power drops.